SpeamCore module · compliance
You know you have obligations. Do you know which of them you could prove today?
The KRITIS module keeps the obligation catalog, assessments, evidence, measures and reporting deadlines in one place — for the physical protection of critical facilities under the German KRITIS Act and the EU CER Directive.
24 h
reporting clock for the initial report
47
BSI elementary threats in the risk assessment
9
sector profiles in the catalog
Three sentences you hear in almost every company
"It's somewhere in our files."
Inspection reports, maintenance records and operating instructions are spread across drives, binders and mailboxes. Before an audit, collecting them takes days.
"Is this still current?"
The KRITIS Act, CER and NIS2 keep moving. A self-maintained list has no idea a requirement has changed.
"Who actually owns this?"
Without an owner and a deadline, every obligation stays an intention. Only the assignment turns it into a traceable process.
A maintained obligation catalog. And everything attached to it.
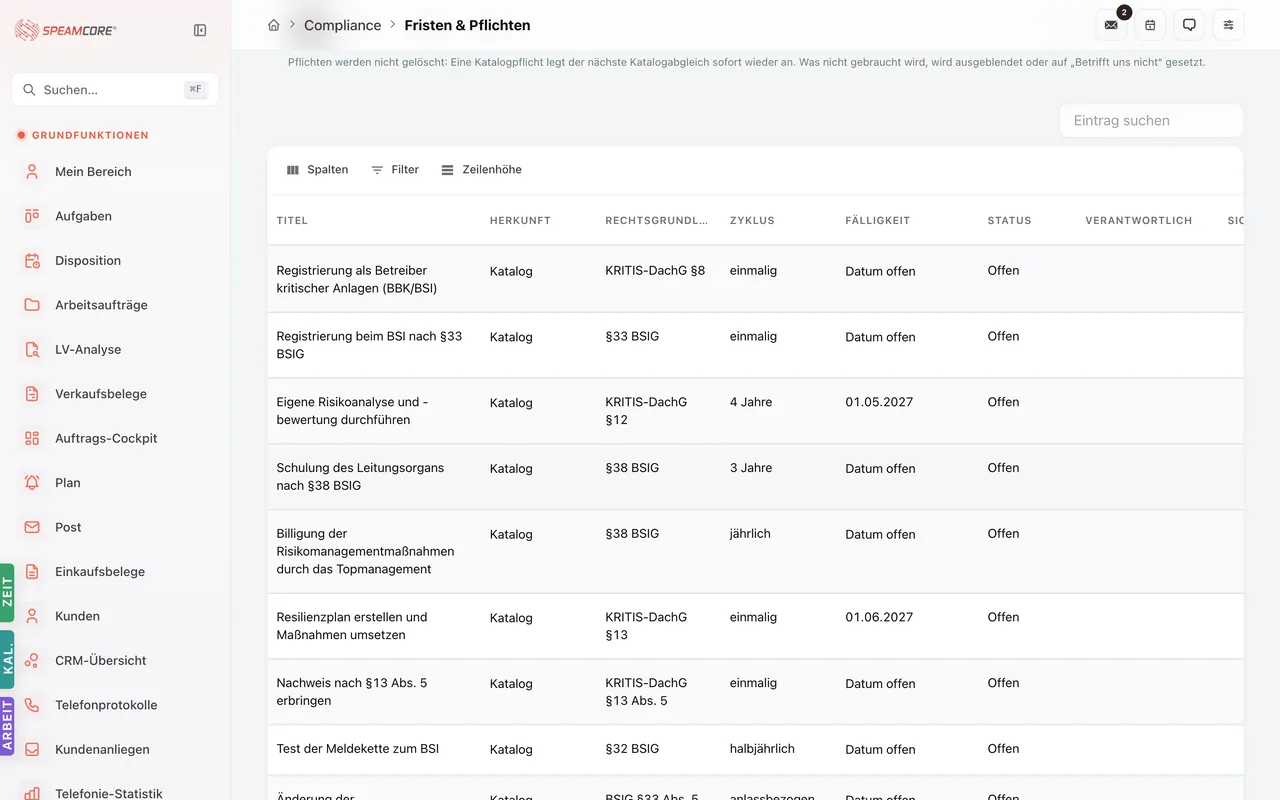
Deadlines and obligations
Every obligation with its legal basis
Every item carries its legal reference, cycle and anchor date. The timeline shows what is due within 30 days and what is overdue — from the quarterly contact list review to the three-year resilience report.
Checks and maturity
Four assessments per site
Maturity check, 100-point audit, sabotage protection audit with knock-out criteria and the risk assessment across the 47 BSI elementary threats — every gap found becomes a measure in one click.
Evidence file
Evidence with an expiry date
Inspection report, load test, training record: uploaded, dated, linked to the requirement it proves. When validity expires, the obligation reopens automatically.
Action plan
Gaps become tasks
Whatever the catalog, a site walk or the risk assessment flags as a gap becomes a measure with an owner and a due date — as a regular SpeamCore task.
Incidents and reporting deadlines
The 24-hour clock runs with you
A recorded incident starts the reporting clock visibly: initial, interim and final report. The report is prepared in structured form and exported as a PDF — you send it yourself.
Authority report
One click, one PDF
Compliance level, obligation status, measures and evidence coverage with reporting date and catalog version — the version for management, auditors or authorities.
Your risks are not only on your site. They are next to it.
Der Umfeld-Scan legt einen Radius um Ihre geokodierte Standortadresse und ermittelt aus OpenStreetMap, was dort liegt: Umspannwerke, Freileitungen, Bahnstrecken, Tankstellen, Wasserspeicher. Jeder Fund wird als Abhängigkeit oder Gefahr eingestuft — mit Betreiber, Kennung und Entfernung. Sie übernehmen ihn ins Risikoregister oder verwerfen ihn begründet; die Entscheidung bleibt dokumentiert.
The dependency analysis is mandatory. Usually it is done once from local knowledge — here it is traceable, repeatable and documented.
Vespucciweg substation · Netze BW GmbH
Umspannwerk · Abhängigkeit
Stuttgart–Filderstadt, Echterdingen tunnel · DB InfraGO AG
Bahnstrecke · Gefahr
Filling station Echterdinger Straße
Tankstelle · Gefahr
These clocks are already running
Am I in scope for KRITIS?
Three inputs, one assessment. This check is no substitute for legal advice — borderline cases need legal confirmation.
From first call to first authority report
Define the scope
Which sites, which facilities, which sector — that determines the applicable obligation catalog.
Set up the protected object
Create and geocode sites, run the surroundings scan, triage the findings. Five guided steps, not an empty form.
Assign responsibilities
Every obligation gets an owner and a deadline. The most honest moment of the project.
Add your evidence
Map existing documents to the requirements. Whatever is missing then sits in the action plan.
Pull the report
The first authority report shows the real status. From here it is operations, not a project.
We do not write the requirements ourselves.
A specialist KRITIS firm keeps the content current on an ongoing basis — not project by project. When a requirement under the KRITIS Act, CER or NIS2 changes, the catalog changes, and the delta comparison shows which of your evidence is affected. We build the machinery around it: versioning, release, changelog, distribution to every tenant.
Some catalog items reference licensed standards (DVGW, DIN, VdS). The catalog does not quote them, it names the reference — the source register shows the license status per source.
One price, no tiers, no consulting days.
€299.00 / month
plus VAT · three sites included, each additional site €50.00 / month
Compliance module family
One compliance core. One module per regulation.
Desk, evidence file, action plan, incidents and risk register live in the compliance core. Each regulation is added as its own module — you only book what applies to you.
Processes with approvals, internal audits, management review, CAPA and quality objectives.
Information security under §30 BSIG, reporting and supply chain — shares desk, incidents and evidence file with KRITIS.
Physical protection of critical facilities: obligation catalog, checks, site walks, reporting clock.
Information security management system with control catalog and audit preparation.
Digital operational resilience for financial firms and their ICT providers.
Questions we hear often
Does the module replace our auditor?
No. It removes the searching from both sides: the auditor sees the status instead of asking for it. You see in advance what they will ask about.
We already have a spreadsheet. What is the difference?
The spreadsheet knows nothing about deadlines running out, evidence becoming invalid, and nobody updates it when CER or the KRITIS Act change.
Is this about IT security or physical protection?
The focus is physical protection and resilience. Information security gets its own NIS2 module; both share desk, incidents, evidence file and risk register.
Can we use the module for a certification?
Yes. The roadmap for IAPPA certification (KRITIS) and VdS 10000 (NIS2) is included, with steps and document status.
How long does implementation take?
The catalog is there on day one. How long the evidence takes depends on how tidy your documentation is today — which is exactly what the first report shows.
Does the system submit the report to the authority?
No. It prepares the report in structured form and tracks the deadlines. Submitting it through the official channel remains your step.
30 minutes in the real catalog — with your sector, not sample data.
We switch on the obligation catalog for your scope, run the surroundings scan on your address and walk through the result together.